

Chrome Zero-Day Alert: CISA Adds Critical Flaw
The Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent alert for a newly discovered Chrome zero-day vulnerability, tracked as CVE-2026-XXXX.
The Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent alert for a newly discovered Chrome zero-day vulnerability, tracked as CVE-2026-XXXX.

A major US healthcare network is currently grappling with widespread IT outages after the notorious RansomHub ransomware group claimed responsibility for a
In a stunning turn of events, hackers have discovered a new and terrifying way to steal social media accounts. They

Imagine waking up to find your email, password, and every website you’ve ever logged into sitting in a publicly accessible

The WordPress security team has just dropped an emergency security release that every website owner needs to install immediately. Version 6.8.1

The cryptocurrency community is on high alert following a new threat intelligence report from Mandiant. The report reveals that the

The FIFA World Cup 2026 is set to be the largest sporting event in history, spanning 16 cities across the

On June 21, 2026, a chilling reality set in for millions of Californians. It wasn’t an earthquake, a wildfire, or

More than 700 websites built on Ghost CMS have been compromised in a large-scale campaign exploiting a critical vulnerability tracked
The 30,000-Foot ViewFor ten years, they watched. For ten years, they listened. And for ten years, the victim—a major global
For years, cybersecurity experts warned that threat actors would eventually weaponize artificial intelligence. That future is no longer on the
Wireless networks are everywhere. They connect our homes, our offices, our hospitals, and our airports. But wireless signals do not

Imagine waking up and telling your computer to “order my weekly groceries, find the cheapest flight to New York, and

WPA3 and WPA2 are the two most widely deployed Wi-Fi security protocols in use today. While WPA2 has protected billions

Arch Linux AUR breach compromises 400+ packages with Rust infostealer and eBPF rootkit. Malware steals credentials, crypto wallets, and browser

Microsoft fixes 60+ flaws, including two zero days already used in attacks. Update Windows systems immediately to prevent compromise. Microsoft

Critical CVE-2026-35273 allows unauthenticated remote code execution. ShinyHunters exploited it to steal student data from over 100 organizations worldwide. A
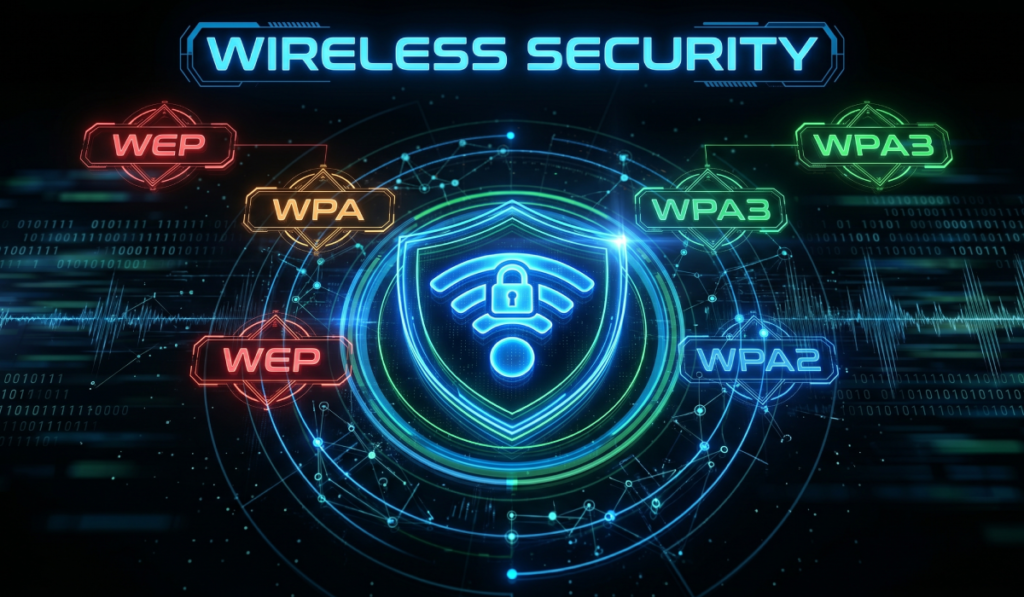
Wireless security is one of the most critical and most overlooked areas of network protection. Every Wi-Fi network — from

The cybersecurity world witnessed a seismic shift this week with Operation Morpheus, a landmark Cobalt Strike takedown that successfully dismantled

You exploited a vulnerability and gained SYSTEM access. But a shell dies on reboot. Maintaining Access in Privilege Escalation ensures

A new local privilege escalation exploit named RoguePlanet is actively bypassing Microsoft Defender on fully updated Windows 10 and Windows

In what cybersecurity experts are calling the most alarming social media breach of the year, a substantial portion of TikTok’s internal

Privilege escalation is one of the most critical skills in penetration testing and one of the most important attack paths

At exactly 3:30 in the morning on March 11, 2026 Something unprecedented happened. It occurred inside the digital infrastructure of one of

Post-exploitation is the phase of a penetration test that begins the moment a successful compromise is achieved. It is where
In late May 2026, a post surfaced on one of the internet’s most active cybercrime forums that sent shockwaves across
Imagine trying to update your smartphone’s operating system. Now imagine that phone is drifting through the icy unknown of interstellar

The Metasploit Framework ships with thousands of built-in modules — but the security community continuously develops new modules for newly
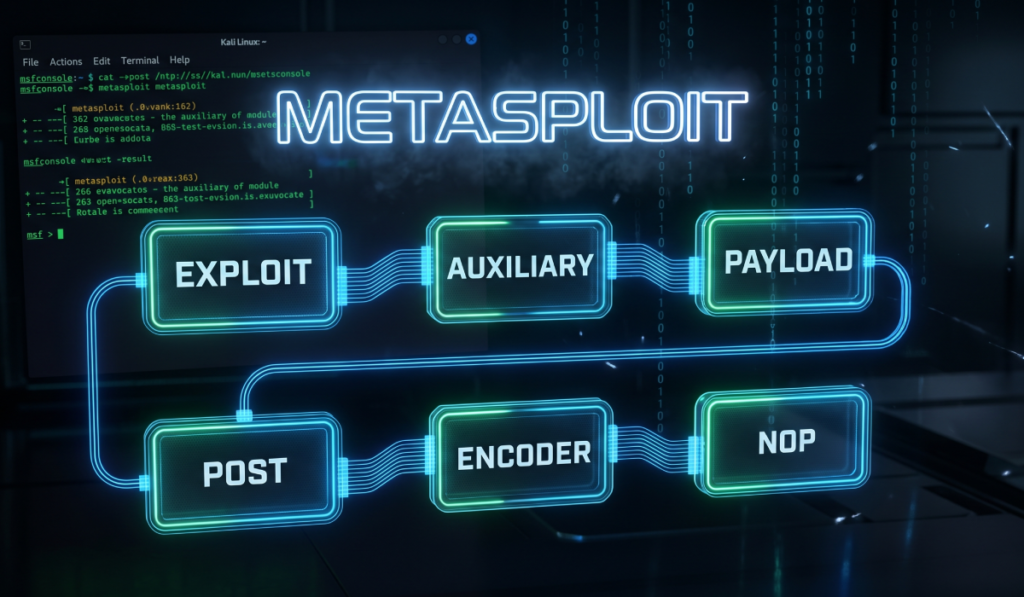
Understanding Metasploit modules is the key to using the framework effectively. Every capability in the Metasploit Framework, from scanning and

What Is Fighting Ursa? Before diving into the attack, let’s understand the adversary. Fighting Ursa (also tracked as APT28, Fancy Bear,

Metasploitable 2 is the safest and most practical way to learn penetration testing. It is a deliberately vulnerable Linux virtual

Hackers exploited Meta’s AI chatbot in a novel account takeover campaign — turning the company’s own Llama-powered assistant into a

For years, endpoint detection and response (EDR) platforms have been the crown jewel of enterprise defense. They watch every process,
The Metasploit Framework is the most powerful open-source penetration testing platform available on Linux. It gives security professionals a consistent,

Google Threat Intelligence Group has confirmed a troubling development. Chinese state-sponsored hackers are actively using Anthropic’s Claude AI to discover

Google Threat Intelligence Group has issued a warning. Specifically, North Korean state-sponsored hackers are now using artificial intelligence to target defense

Google Threat Intelligence Group has confirmed a troubling development. Russian state-sponsored hackers are actively using Google’s own Gemini AI model