Iranian Hackers Infrastructure Breach Alert
A sophisticated cyber campaign has targeted critical infrastructure across multiple US states, with suspected Iranian hackers at the helm. These multi-state cyberattacks represent a
A sophisticated cyber campaign has targeted critical infrastructure across multiple US states, with suspected Iranian hackers at the helm. These multi-state cyberattacks represent a
Wireless networks are everywhere. They connect our homes, our offices, our hospitals, and our airports. But wireless signals do not

WPA3 and WPA2 are the two most widely deployed Wi-Fi security protocols in use today. While WPA2 has protected billions
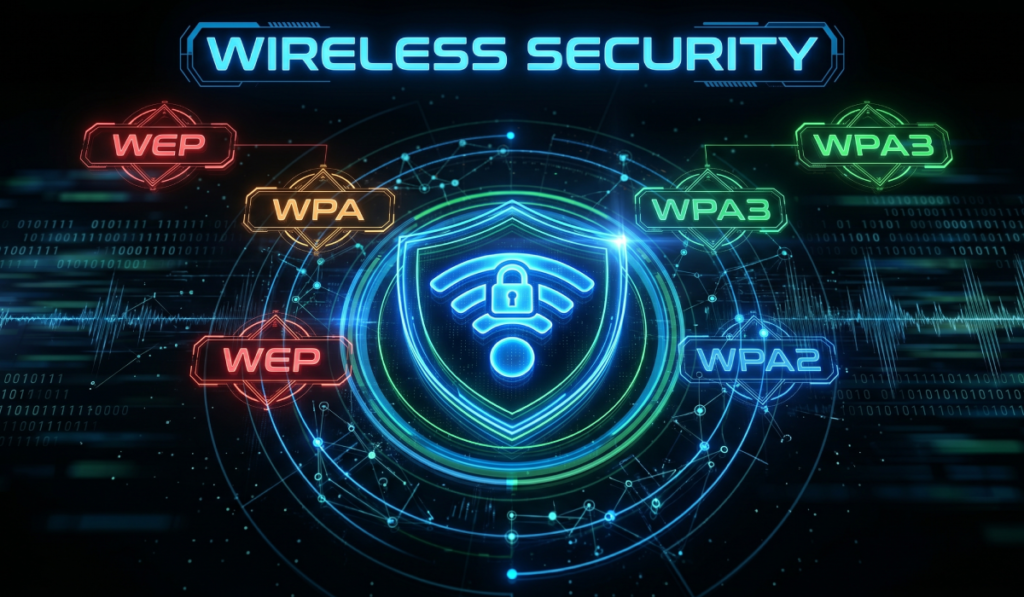
Wireless security is one of the most critical and most overlooked areas of network protection. Every Wi-Fi network — from

You exploited a vulnerability and gained SYSTEM access. But a shell dies on reboot. Maintaining Access in Privilege Escalation ensures

Privilege escalation is one of the most critical skills in penetration testing and one of the most important attack paths

Post-exploitation is the phase of a penetration test that begins the moment a successful compromise is achieved. It is where

The Metasploit Framework ships with thousands of built-in modules — but the security community continuously develops new modules for newly
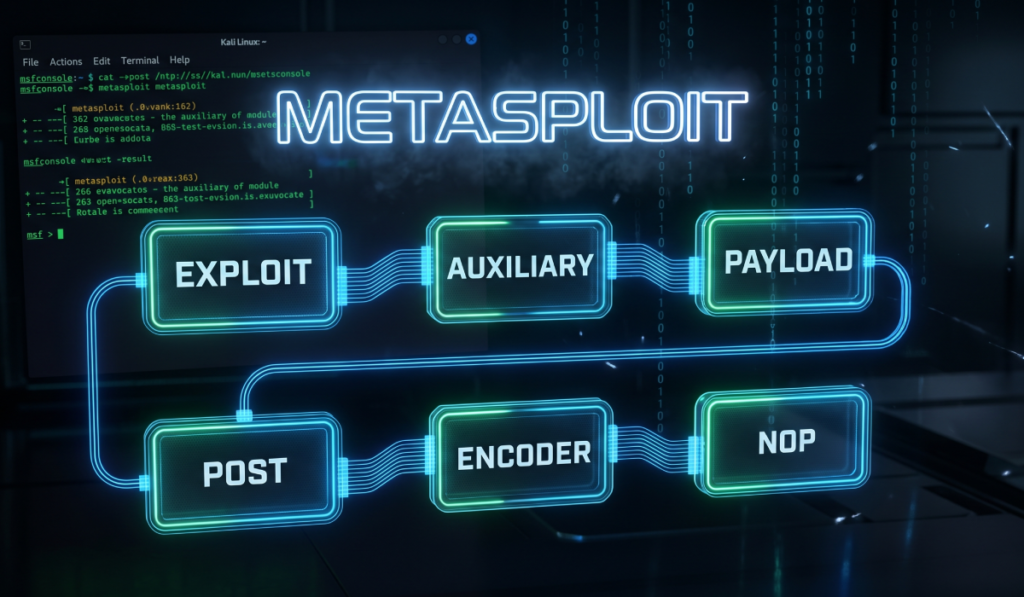
Understanding Metasploit modules is the key to using the framework effectively. Every capability in the Metasploit Framework, from scanning and

Metasploitable 2 is the safest and most practical way to learn penetration testing. It is a deliberately vulnerable Linux virtual
The Metasploit Framework is the most powerful open-source penetration testing platform available on Linux. It gives security professionals a consistent,
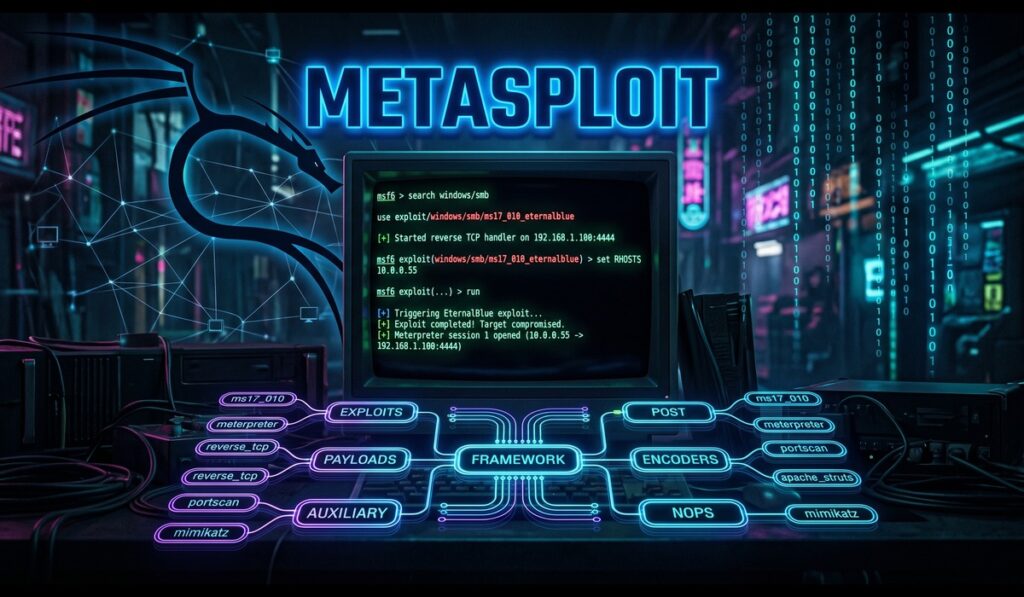
Metasploit is the world’s most widely used penetration testing framework. It gives security professionals a structured, modular platform to discover

Nikto is a free, open-source web server scanner written in Perl by Chris Sullo. Pre-installed in Kali Linux, it tests

Gobuster is one of the most essential web application reconnaissance tools in Kali Linux. It discovers hidden directories, files, DNS

Nmap — short for Network Mapper — is the most widely used network discovery and security auditing tool in the
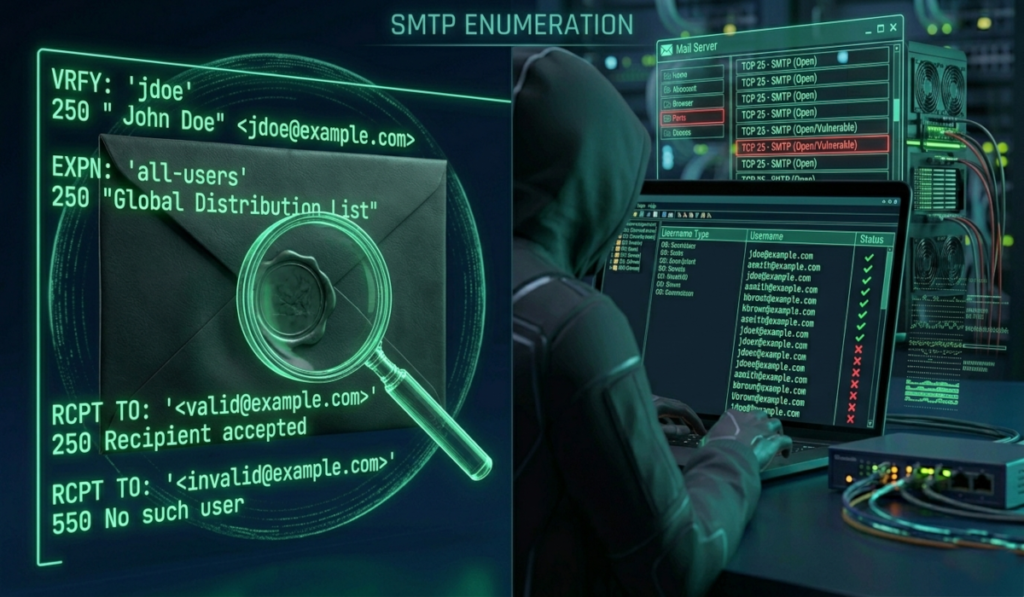
SMTP enumeration extracts valid usernames and email addresses directly from a mail server using the server’s own built-in commands. Every

LDAP enumeration extracts the organisational blueprint of an entire Windows domain, including every user account, group membership, computer object, organisational
SNMP enumeration is one of the most underestimated intelligence gathering techniques in internal network assessments. When a network device responds

SMB enumeration is a highly productive internal penetration testing technique that queries the Server Message Block protocol on port 445
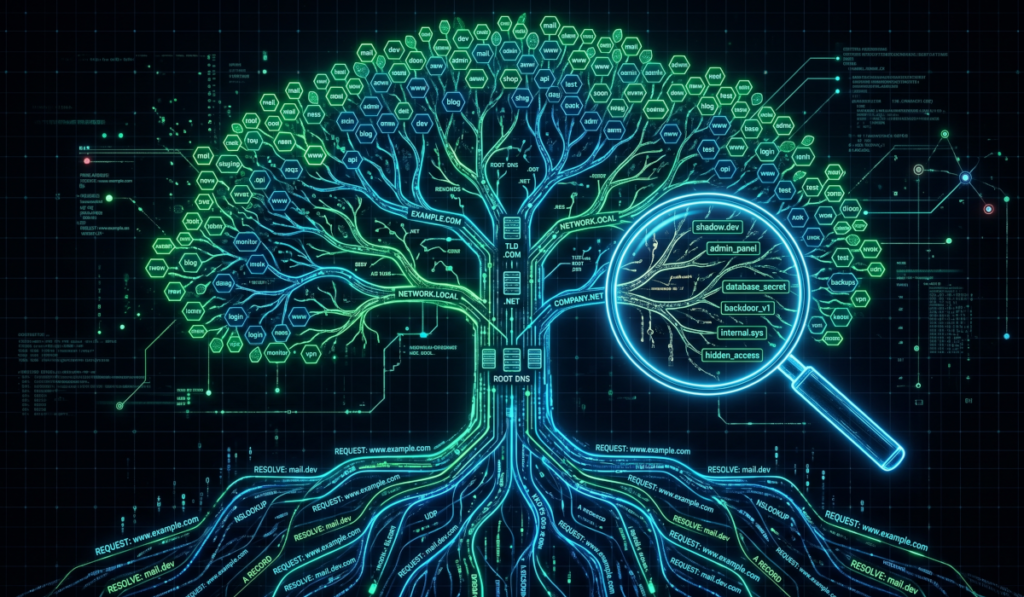
DNS enumeration is a high-value ethical hacking reconnaissance technique that maps a target organization’s internet infrastructure using only publicly accessible
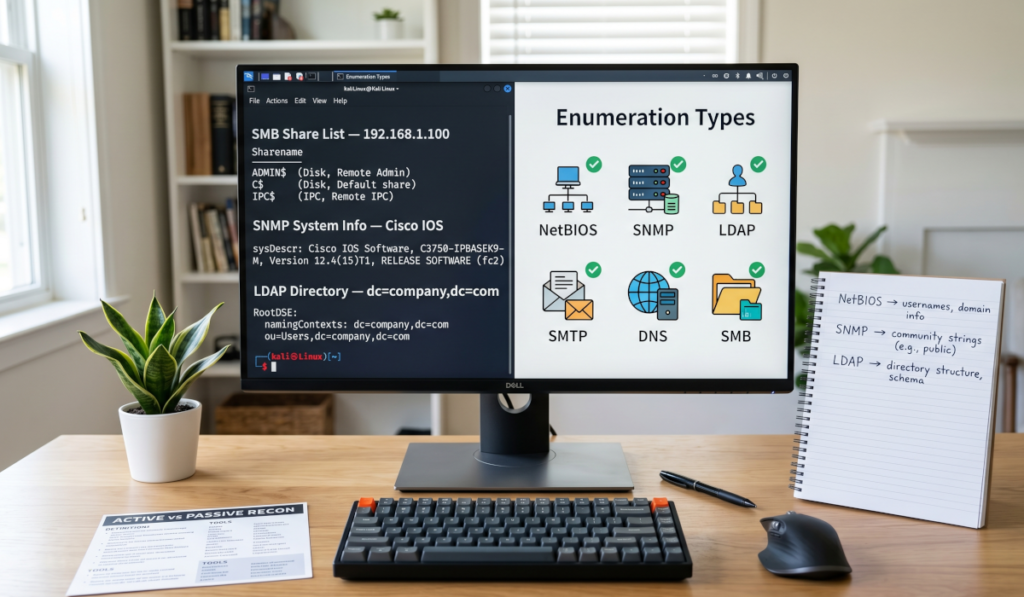
Enumeration is one of the most precise and intelligence-rich phases in ethical hacking. It moves beyond identifying what is running

Malware scanning is one of the most fundamental defences in modern cybersecurity. It protects individuals, businesses, and government organisations from

Vulnerability scanning is one of the most critical steps in any security assessment. It moves beyond knowing which ports are

Nmap scans are the starting point of almost every network security assessment. Whether you are discovering open ports on a

Port scanning in ethical hacking is the process of sending network packets to a target host to discover which TCP

OSINT techniques are the foundation of every professional reconnaissance engagement. Open Source Intelligence transforms publicly available data into actionable security
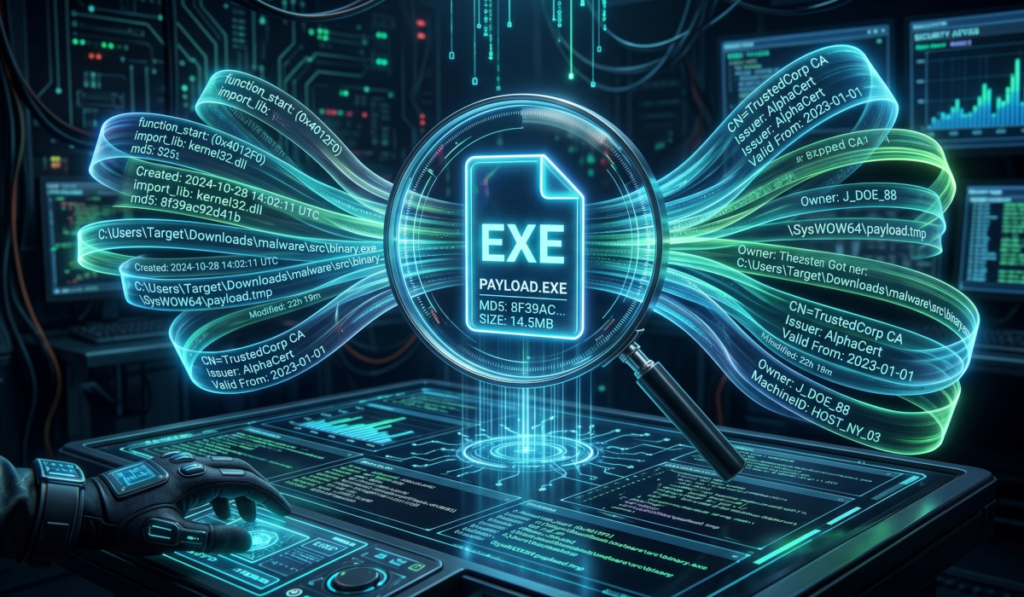
Every executable file carries hidden layers of information beyond its visible function. Metadata extraction from executables uncovers embedded resources, developer

Google Dorking – also called Google hacking – is the technique of using advanced search operators to find sensitive information

Reconnaissance is more than a checklist. It is a discipline, a mindset, and the most critical investment an ethical hacker

WHOIS footprinting is a powerful passive reconnaissance technique in ethical hacking. It uncovers a target domain’s registration details, ownership information,

Before a surgeon operates, they study scans. Before an architect builds, they survey the land. Before an ethical hacker attacks,
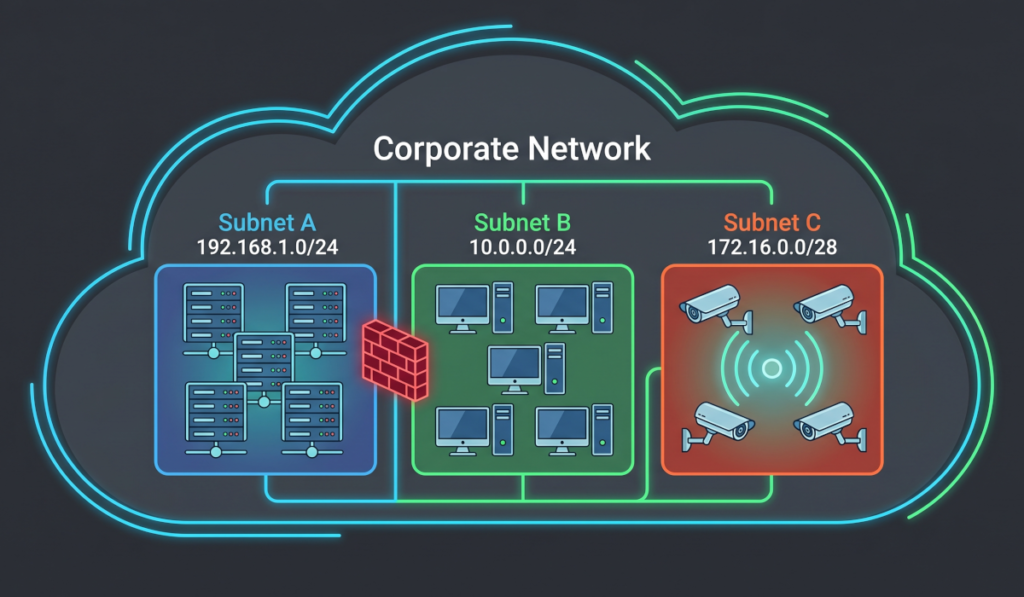
Imagine a large office building with hundreds of rooms and no signage. Finding a specific room would be chaotic, deliveries

SSH keys are cryptographic credentials that let you log into remote servers securely without ever typing a password, offering a

FTP, or File Transfer Protocol, is one of the oldest internet protocols, created in 1971 to move files between computers,

ARP is the protocol that bridges IP addresses and MAC addresses on a local network. Without ARP, no device on

HTTP and HTTPS are the foundation of all web communication. The difference between them, a single letter and a TLS
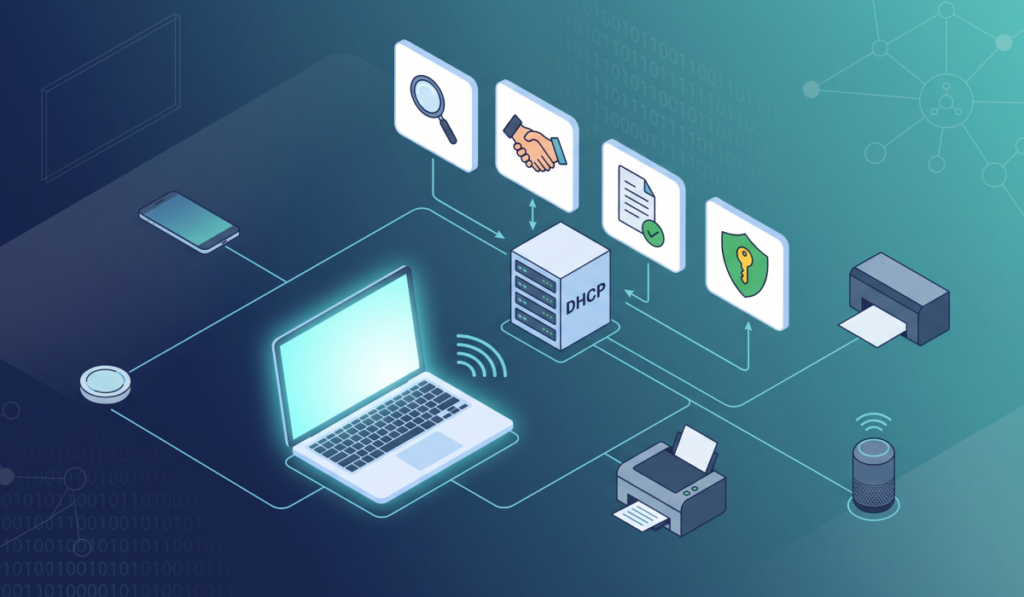
DHCP is the protocol that automatically assigns IP addresses and network configuration to every device that joins a network. Without

DNS is the internet’s phone book translating human-readable domain names into the IP addresses computers use to communicate. It is

TCP/IP ports are the numerical addresses that direct network traffic to the correct application on a host. Knowing which ports
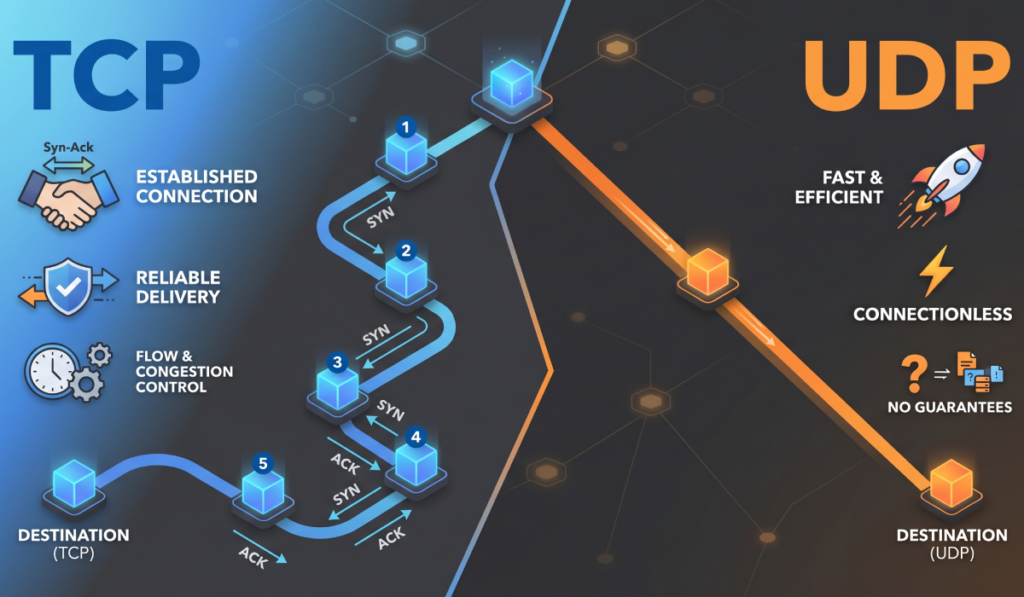
TCP and UDP are the two transport layer protocols that carry nearly all internet traffic, making choosing between them a
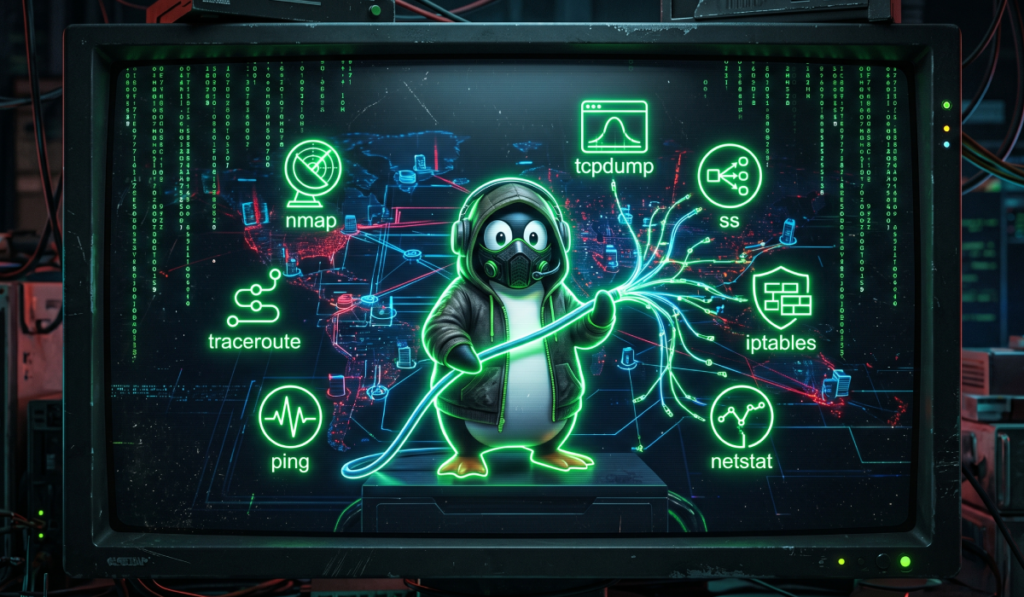
Linux networking commands are the tools that let you configure interfaces, inspect traffic, map networks, and diagnose connectivity – all
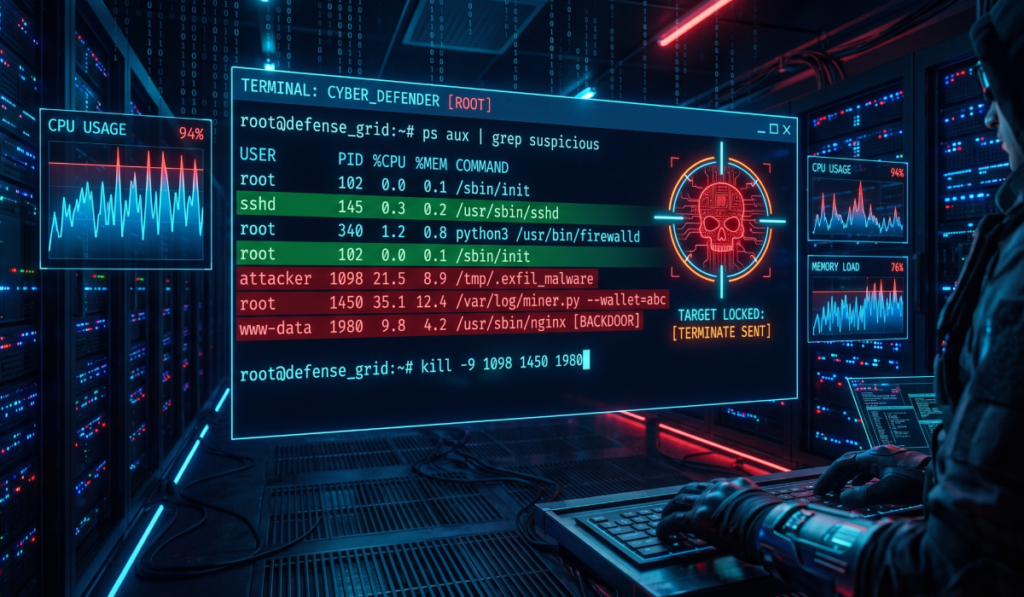
Every program running on a Linux system is a process. Understanding how Linux creates, manages, monitors, and terminates processes is
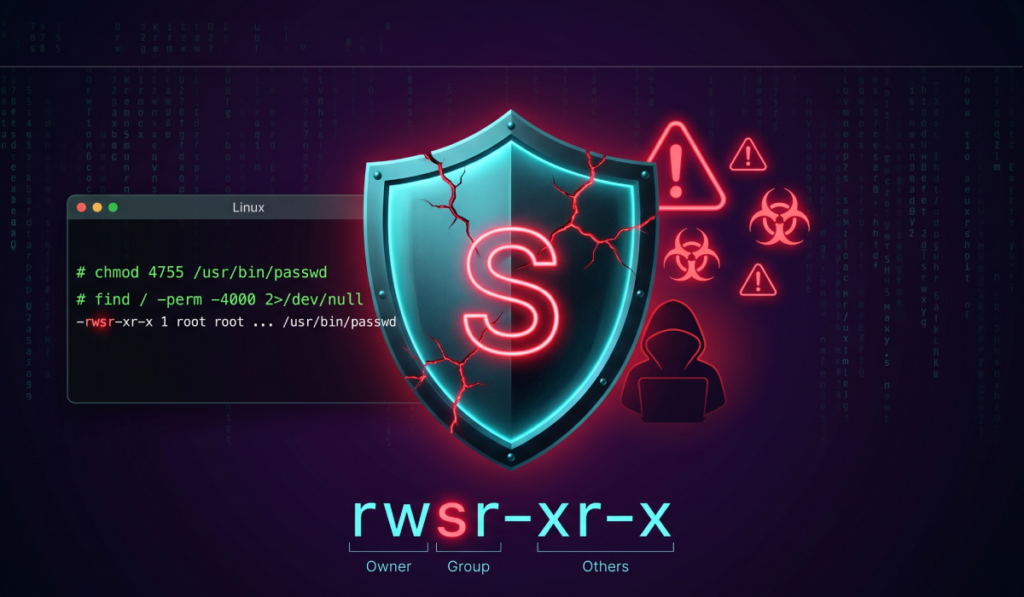
Linux file permissions are the access control system that determines who can read, write, or execute every file and directory

Linux user management controls who can access a system, what they can do, and where they can go. For ethical
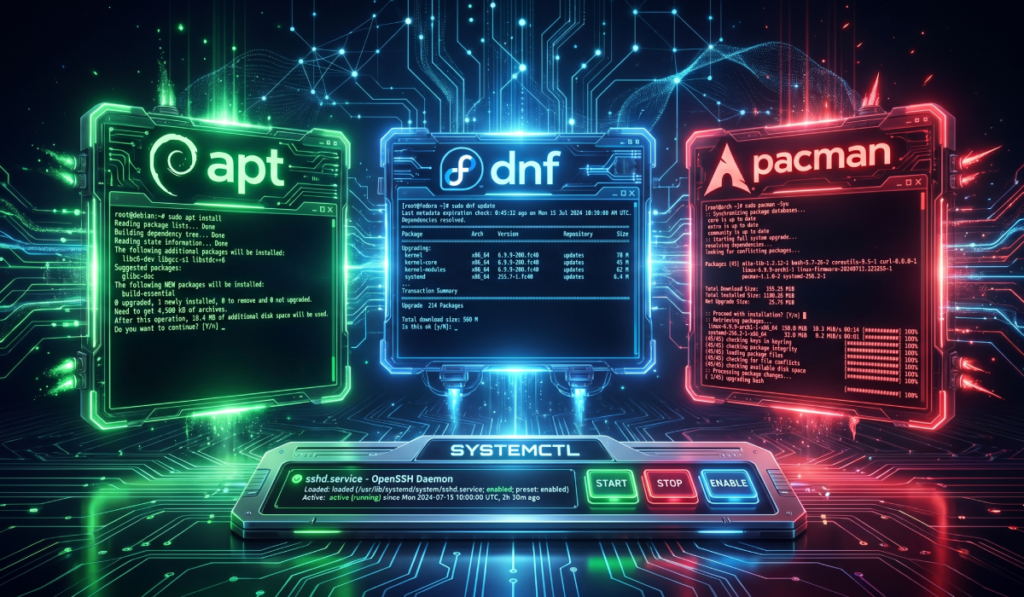
Package managers and systemctl are two of the most essential tools in Linux. One controls what software lives on your

The Linux file system is the organized hierarchy that determines how files, processes, devices, and user data are stored and

The TCP/IP model is the practical framework that governs all communication on the Internet. Unlike the OSI model — which

The OSI model is the universal framework for understanding how data travels across a network — from the application on

Cryptography is the science of securing information by transforming it into an unreadable format — and it underpins virtually every

These three terms are used constantly in cybersecurity — often interchangeably, and almost always incorrectly. Understanding the precise difference between
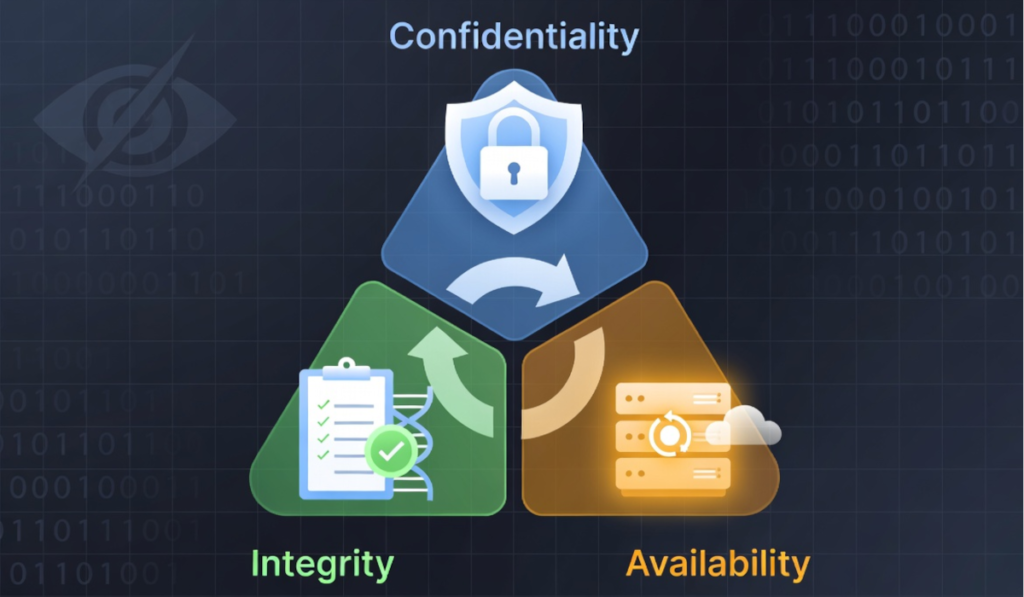
The CIA triad is the foundational model of information security. Every security control, policy, and technology an organization deploys ultimately

Reconnaissance in ethical hacking: passive vs active Reconnaissance is Phase 1 of the 5 phases of hacking — and the

5 phases of hacking explained: a deep-dive guide for cybersecurity learners Every cyberattack follows a structured lifecycle. Understanding the 5

Ethical hackers follow a structured methodology to simulate real-world attacks. These five phases form the backbone of any professional penetration