
SMB enumeration is a highly productive internal penetration testing technique that queries the Server Message Block protocol on port 445 to extract actionable intelligence from Windows environments. This process reveals usernames, group memberships, share names, password policies, and operating system details that directly enable further exploitation. Since SMB is widely deployed as the backbone of Windows file sharing and Active Directory communication, discovering port 445 open during a network scan makes SMB enumeration one of the first and most valuable techniques applied in any internal engagement.
Think of SMB enumeration like approaching the reception desk of a large office building and politely asking every question the receptionist is configured to answer. Some receptionists share everything — usernames, floor layouts, and meeting schedules. Others are restricted. The goal is to ask the right questions and record everything they willingly provide before asking for a key to any rooms.
SMB enumeration tools with practical examples
enum4linux | free
The most comprehensive Windows SMB enumeration tool
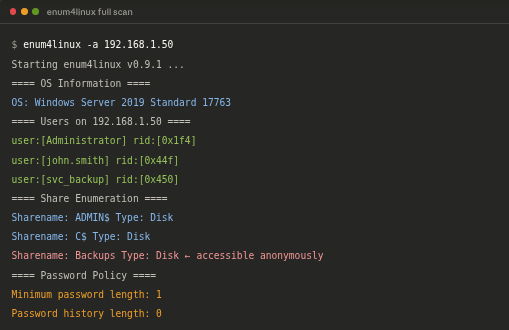
enum4linux is the go-to tool for extracting everything SMB and NetBIOS can reveal — usernames, groups, shares, password policy, OS details, and domain membership in a single command. It wraps multiple Samba utilities and presents a structured, readable output.
smbclient free
Interactive SMB share browser and file access
smbclient connects directly to an SMB share like an FTP client. It is used to list shared contents, browse directories, and download files. An anonymous (null session) connection with no credentials often reveals shared contents on misconfigured systems.

Nmap SMB Scripts (NSE) | free
Automated SMB vulnerability and enumeration checks
Nmap’s Scripting Engine includes a powerful library of SMB-specific scripts. They check for vulnerabilities, enumerate shares and users, detect OS versions, and identify whether critical flaws like EternalBlue are present on the target.

CrackMapExec (CME) | free
Advanced SMB enumeration and credential testing
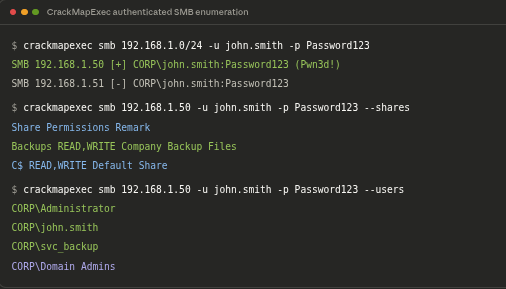
CrackMapExec is the most powerful SMB enumeration tool for authenticated assessments. Once valid credentials are found, it rapidly enumerates the entire Active Directory environment, lists logged-on users, dumps SAM databases, and tests credentials across multiple hosts simultaneously.
What SMB enumeration reveals and its severity
Common SMB enumeration findings and their risk level
| Anonymous access to shares | Critical | Any share accessible without credentials may contain configuration files, backup archives, password files, or database dumps directly downloadable by an unauthenticated attacker. |
| Weak password policy | Critical | A minimum password length of zero or one and no account lockout policy makes the environment fully vulnerable to password spraying attacks against every enumerated user account. |
| EternalBlue vulnerable | Critical | MS17-010 allows unauthenticated remote code execution as SYSTEM. This is the vulnerability used by WannaCry and NotPetya and remains present on unpatched SMB 1.0 hosts. |
| User account exposure | High | Enumerating valid usernames without credentials provides a complete list for password spraying, brute-force, and phishing campaigns targeting the organisation. |
| SMB signing disabled | High | Without SMB signing enforced, the environment is vulnerable to SMB relay attacks where authentication is intercepted and replayed to gain access to other hosts without cracking a password. |
| OS version disclosure | Medium | Knowing the exact Windows Server version allows precise CVE lookups and narrows exploitation to version-specific vulnerabilities, saving significant time during the exploitation phase. |
A minimum password length of 1 combined with no account lockout policy and a full user list from SMB enumeration is an immediate password spraying opportunity. Using a single common password such as the company name against every enumerated account almost always succeeds in at least one login on a misconfigured enterprise domain.
The complete SMB enumeration workflow for an internal penetration test is: confirm port 445 open with Nmap, run enum4linux for full baseline enumeration, use smbclient to browse accessible shares and download files, check for EternalBlue with the smb-vuln-ms17-010 NSE script, and escalate to CrackMapExec once credentials are obtained for domain-wide coverage.
Legal requirement. SMB enumeration establishes active connections to target systems and generates authentication and connection logs. Performing SMB enumeration against any host without explicit written authorisation from the system owner is illegal under computer misuse and fraud legislation in most jurisdictions. Always operate within a signed and agreed scope of engagement.

